Cybersecurity Infographic Series · Application and Software Security
Software Supply Chain Security (Later edition)
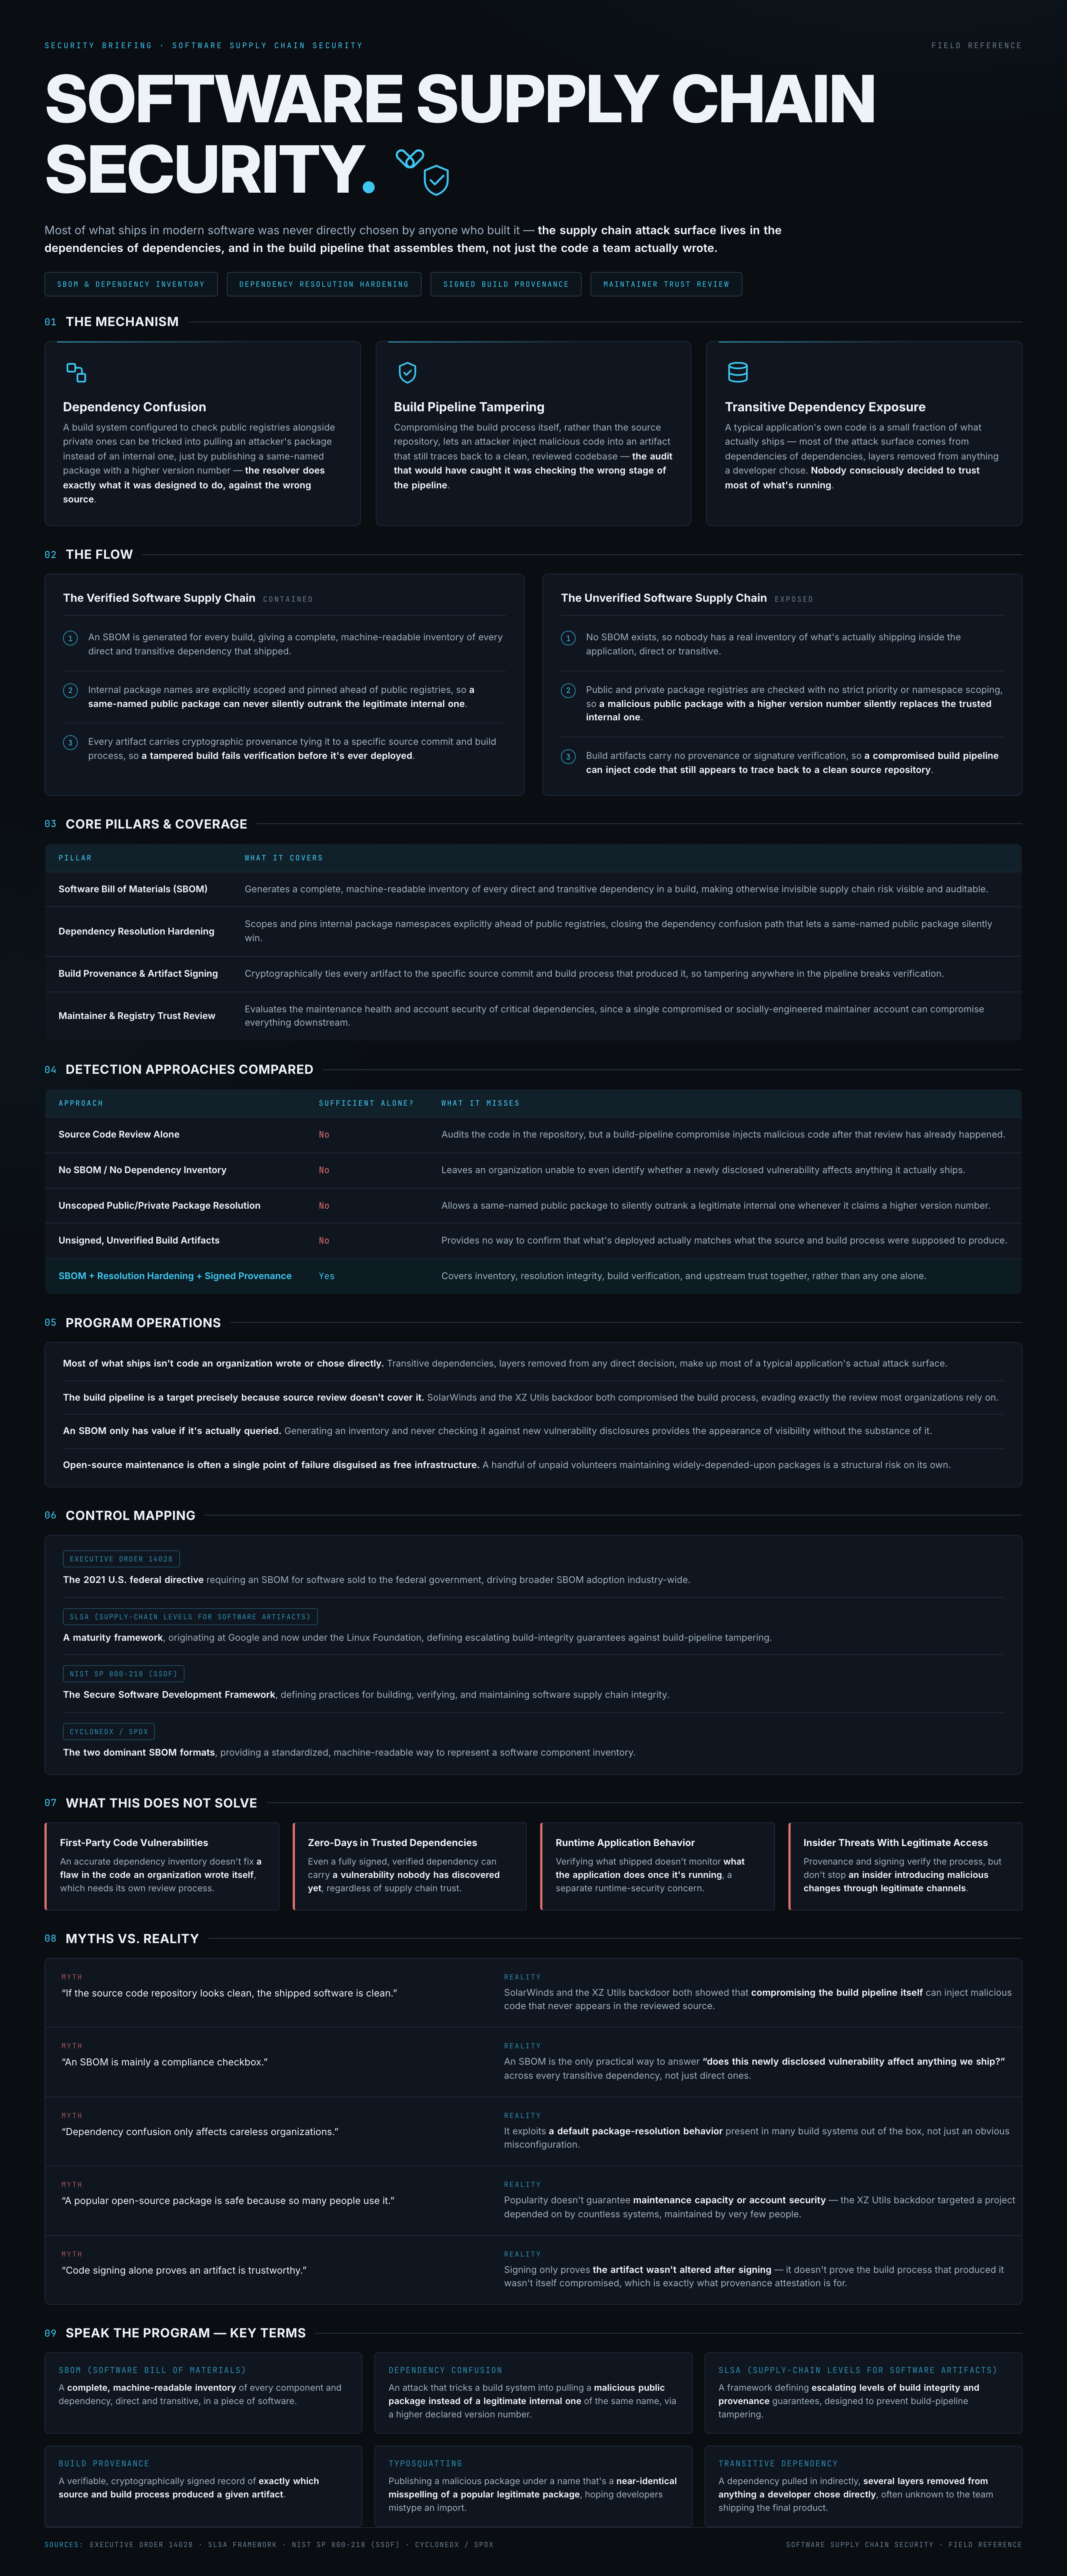
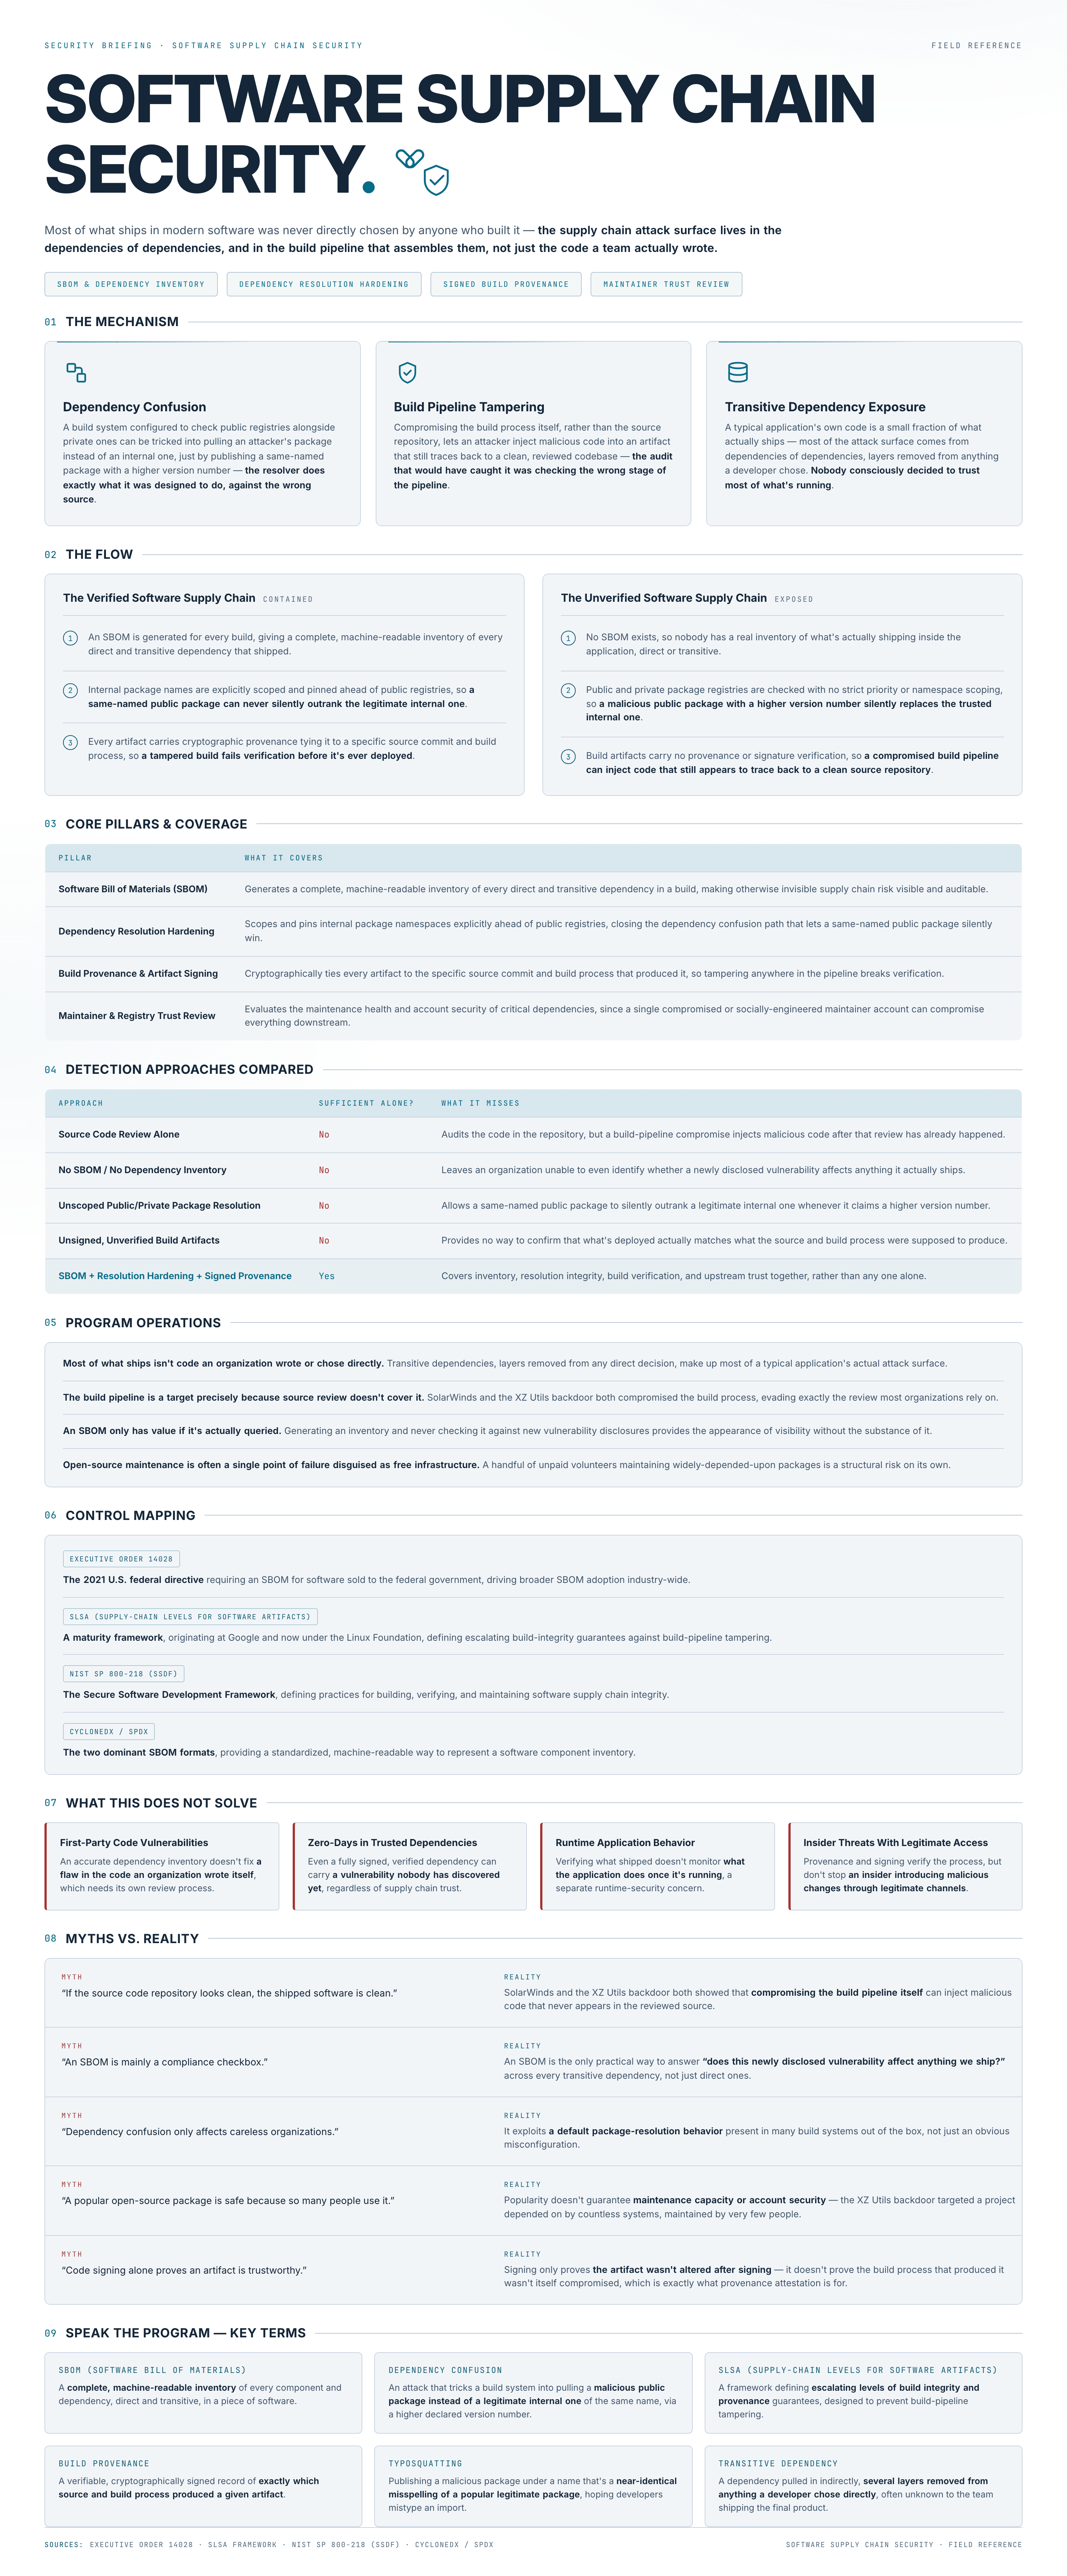
Most of what ships in modern software was never directly chosen by anyone who built it — the supply chain attack surface lives in the dependencies of dependencies, and in the build pipeline that assembles them, not just the code a team actually wrote.
Downloads
- Infographic (PNG, 2880×6952, 1.6 MB)
- Field reference (PDF, 2 sheets, 471 KB)
- Infographic, light edition (PNG, 1.7 MB)
- Field reference, light edition (PDF, 476 KB)
Free to download, no sign-up. Topic 80 of 92 in the series.