Cybersecurity Infographic Series · Identity and Access Security
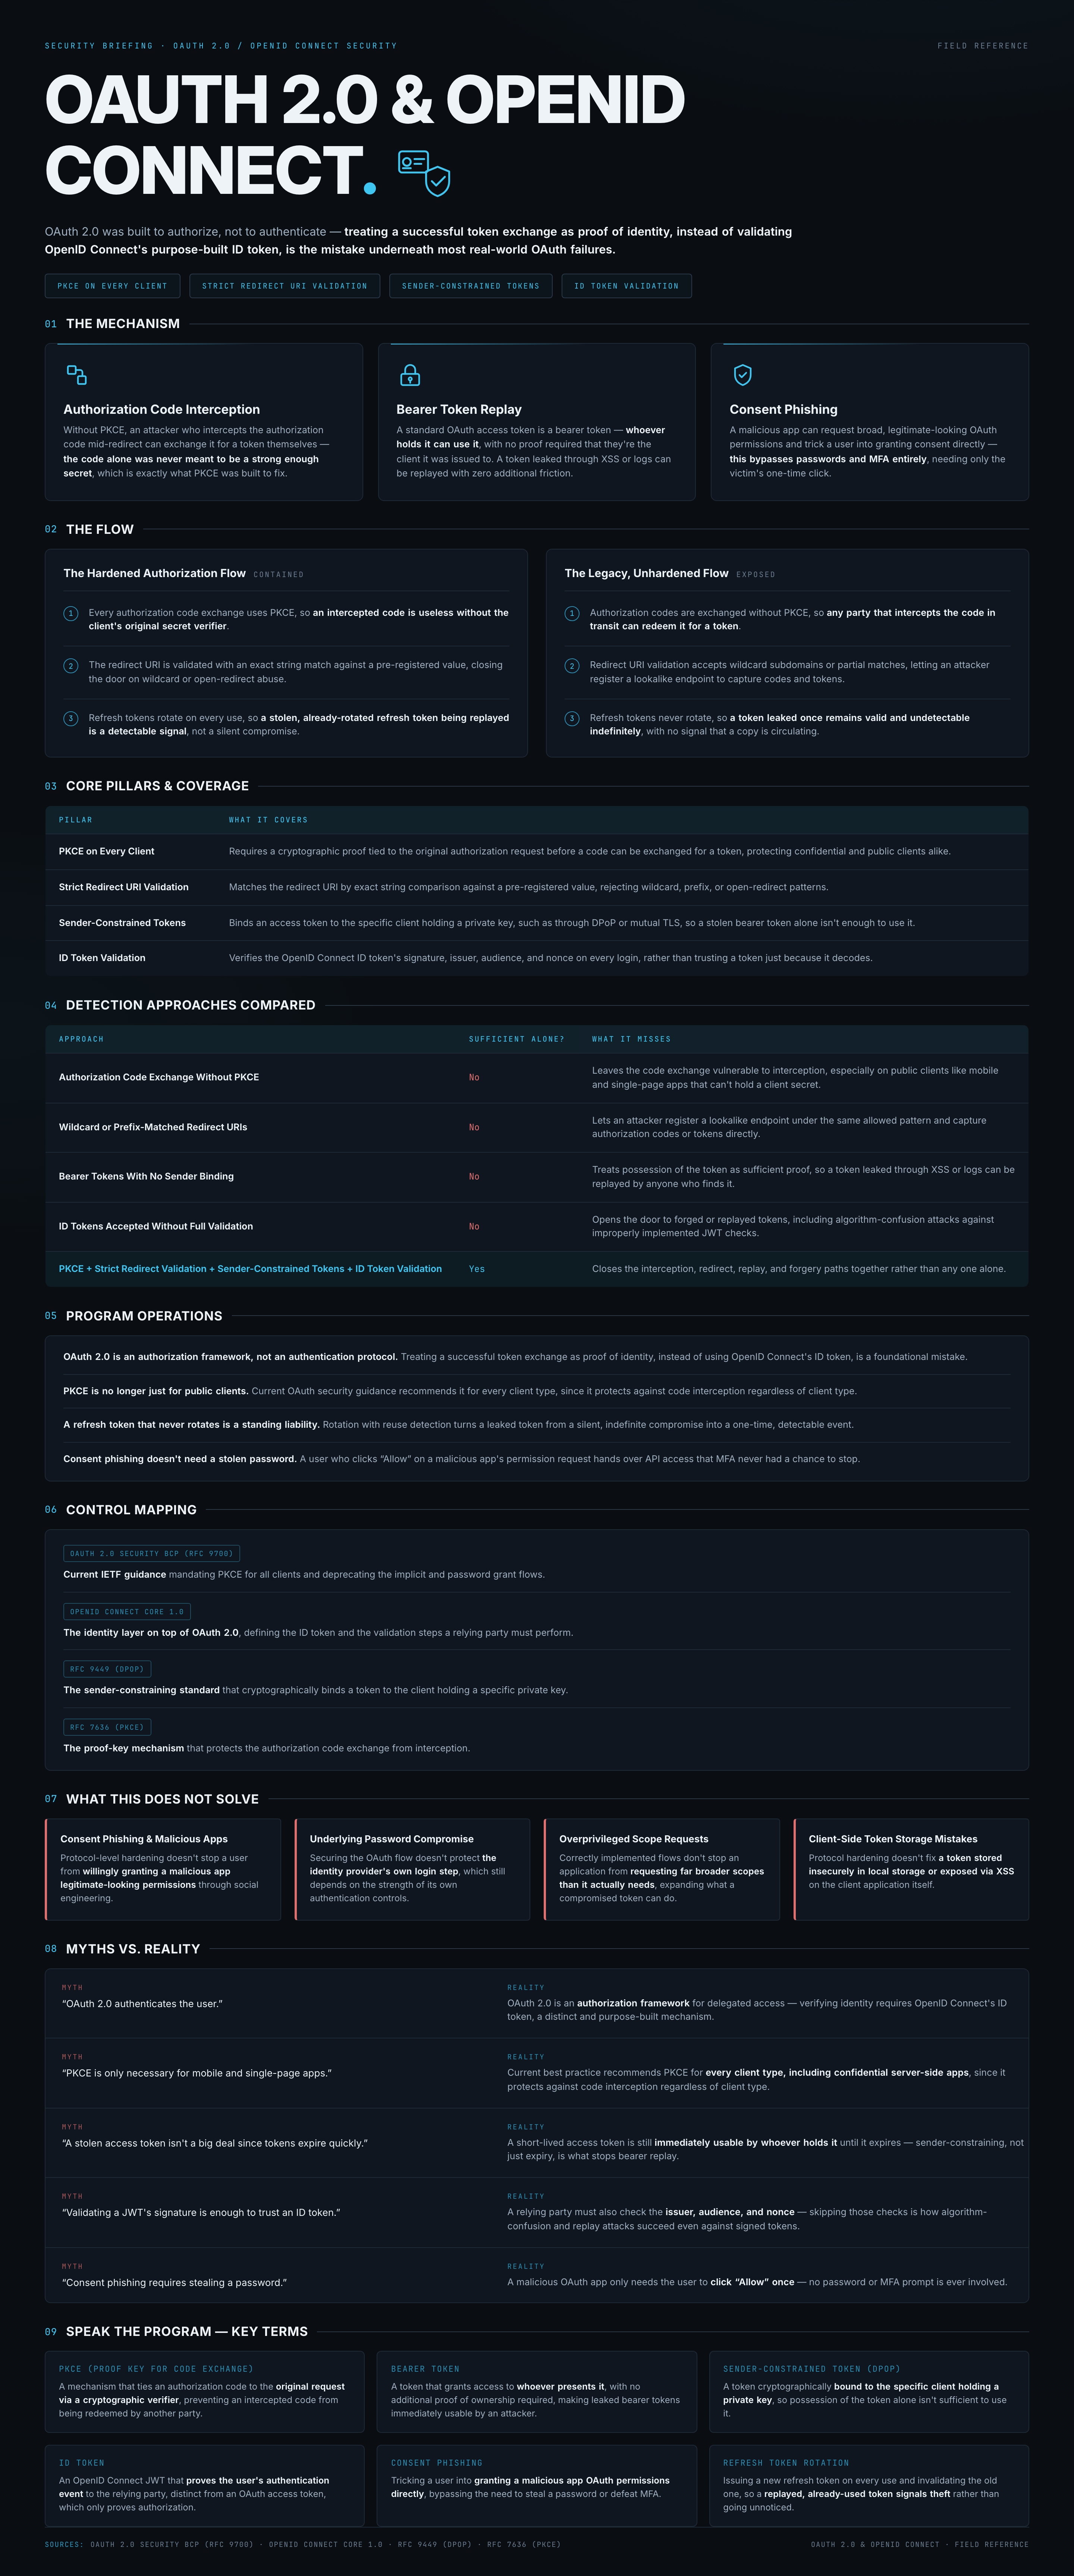
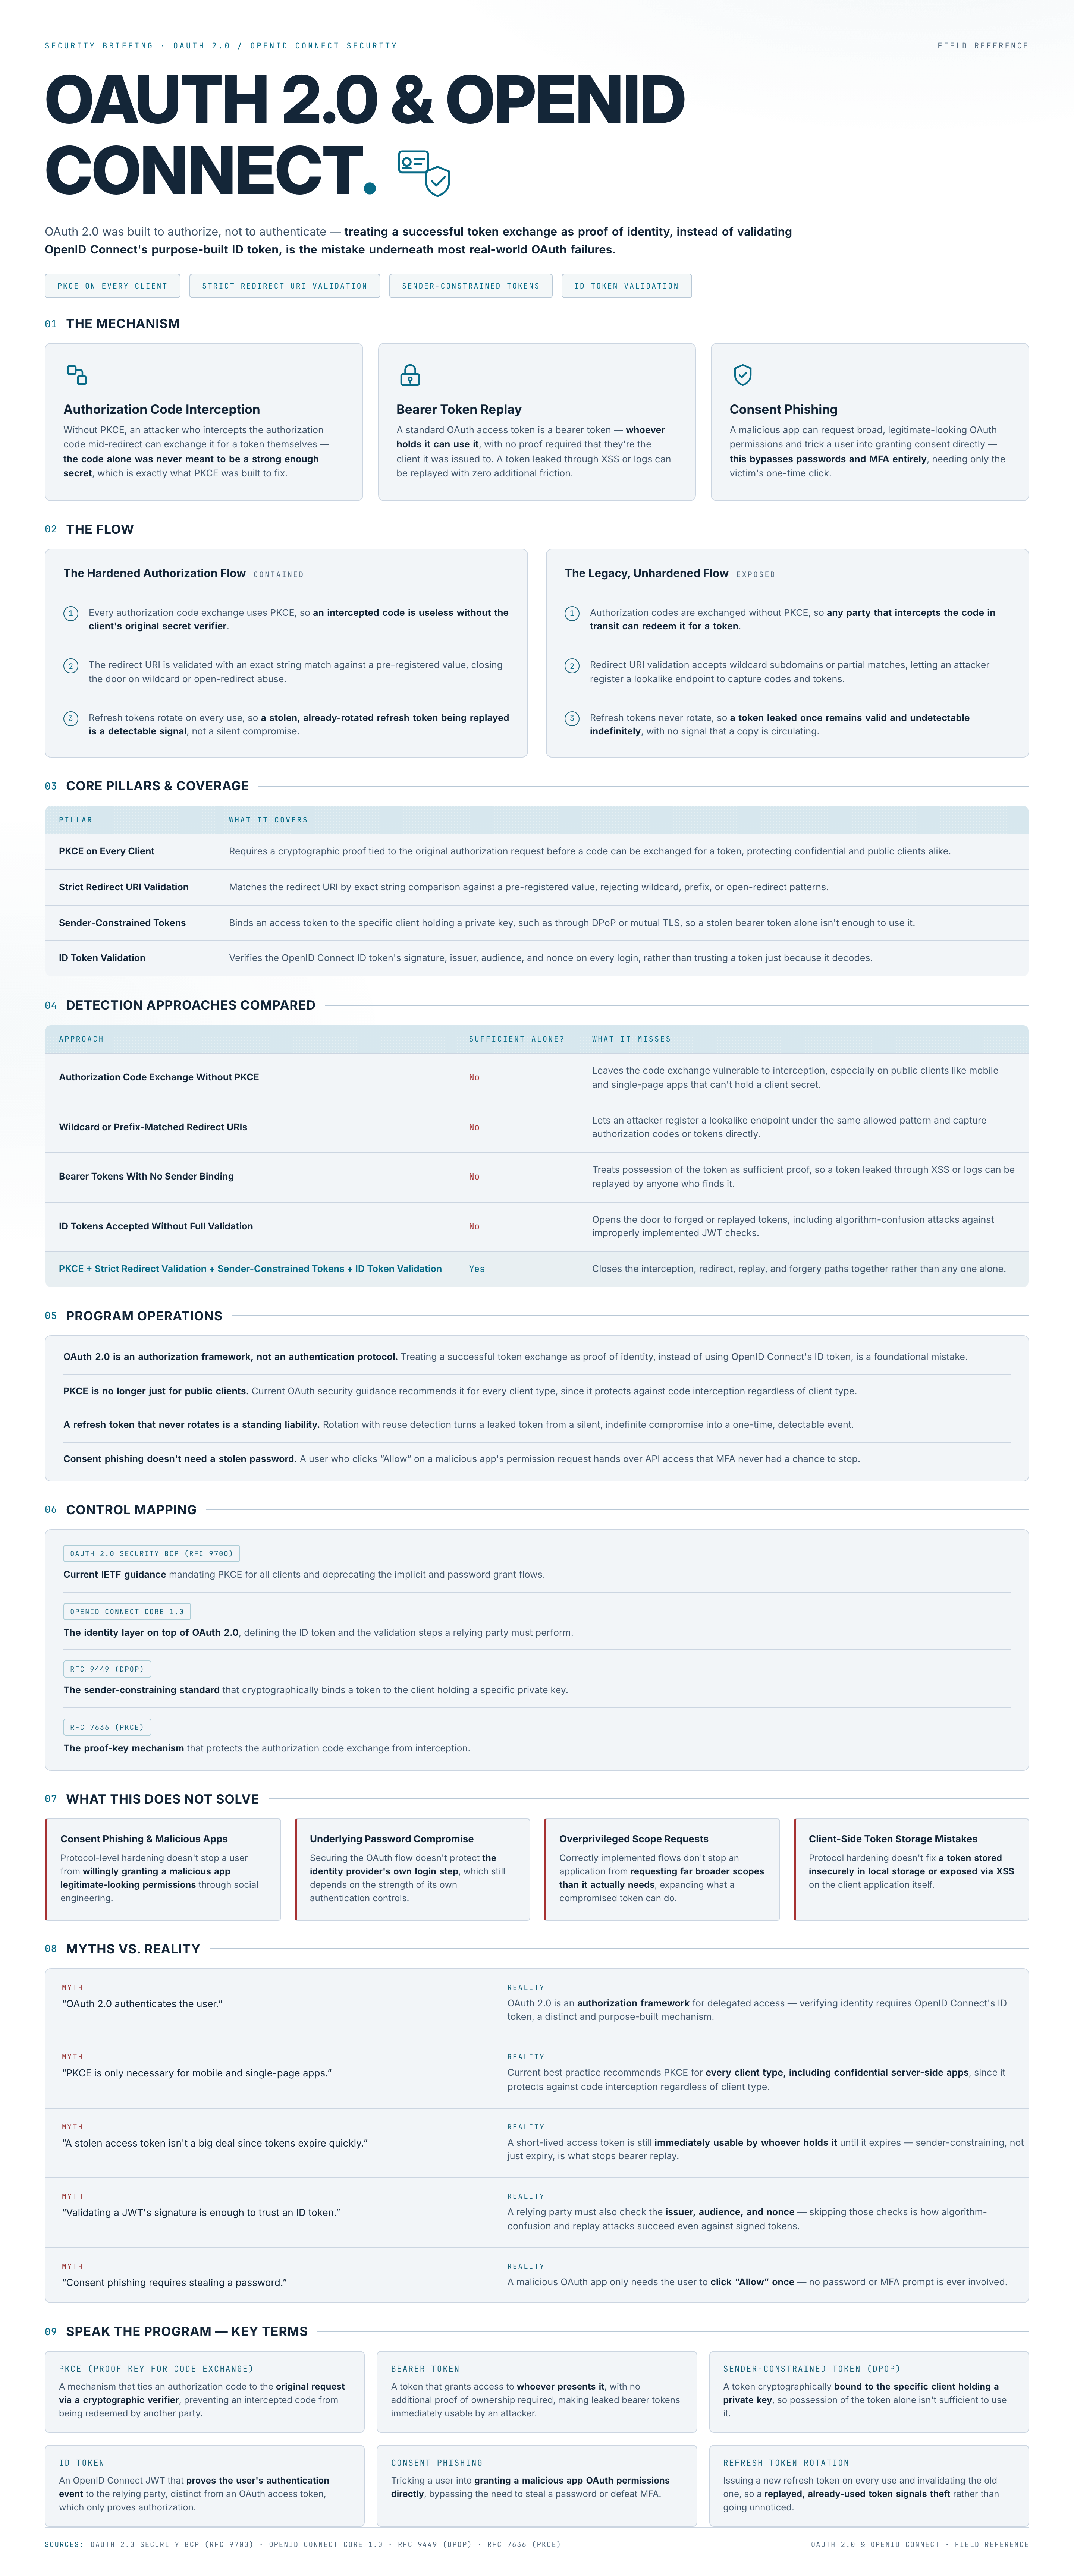
OAuth 2.0 and OpenID Connect Security
OAuth 2.0 was built to authorize, not to authenticate — treating a successful token exchange as proof of identity, instead of validating OpenID Connect's purpose-built ID token, is the mistake underneath most real-world OAuth failures.
Downloads
- Infographic (PNG, 2880×6910, 1.6 MB)
- Field reference (PDF, 2 sheets, 491 KB)
- Infographic, light edition (PNG, 1.6 MB)
- Field reference, light edition (PDF, 495 KB)
Free to download, no sign-up. Topic 77 of 92 in the series.