Cybersecurity Infographic Series · Cloud and Container Security
Container and Kubernetes Security (Later edition)
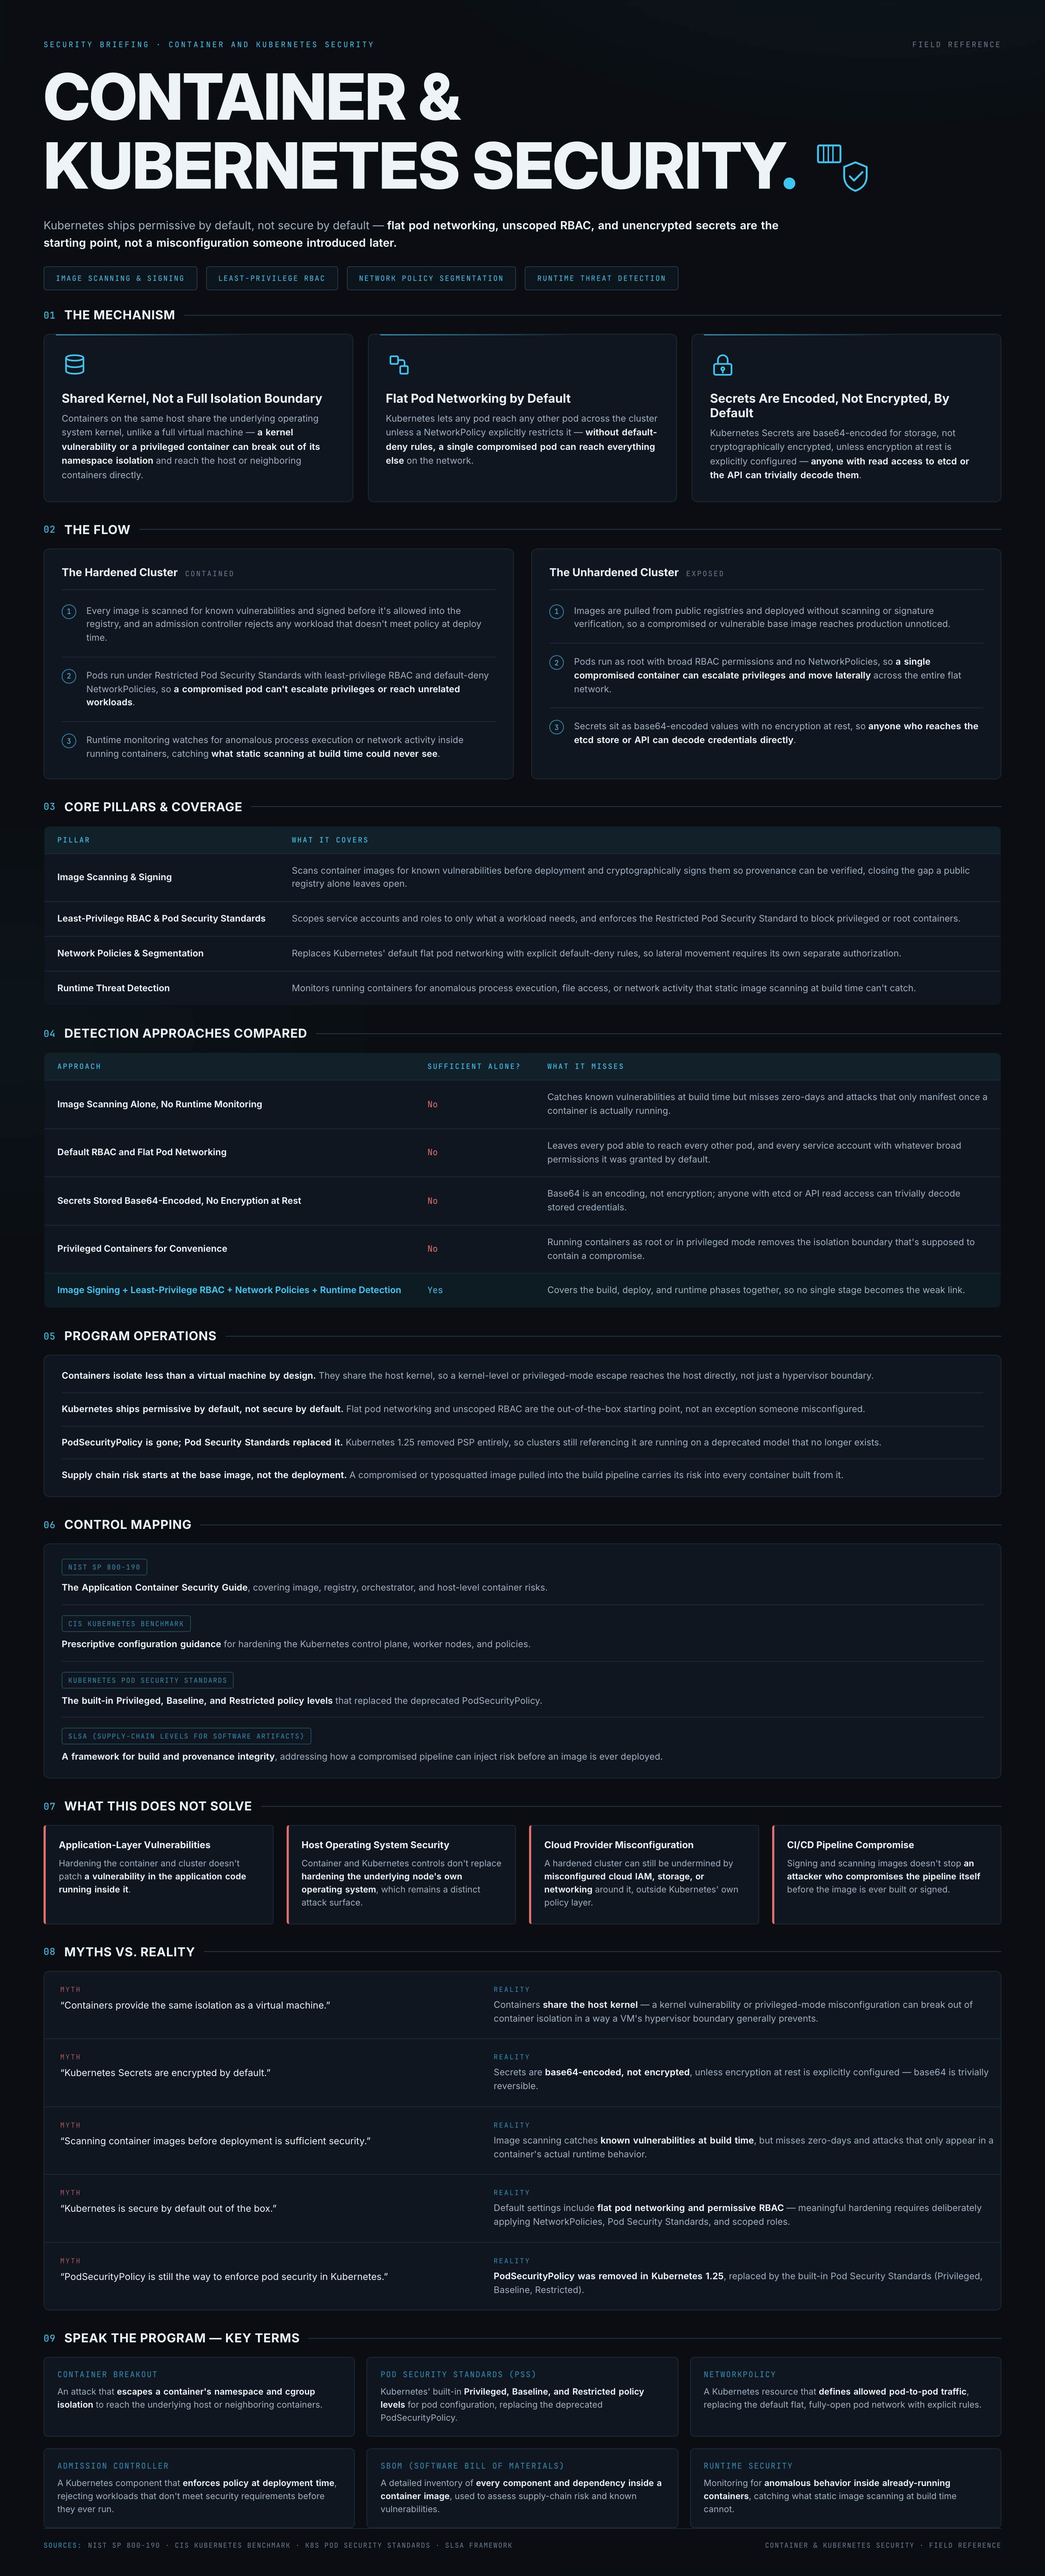
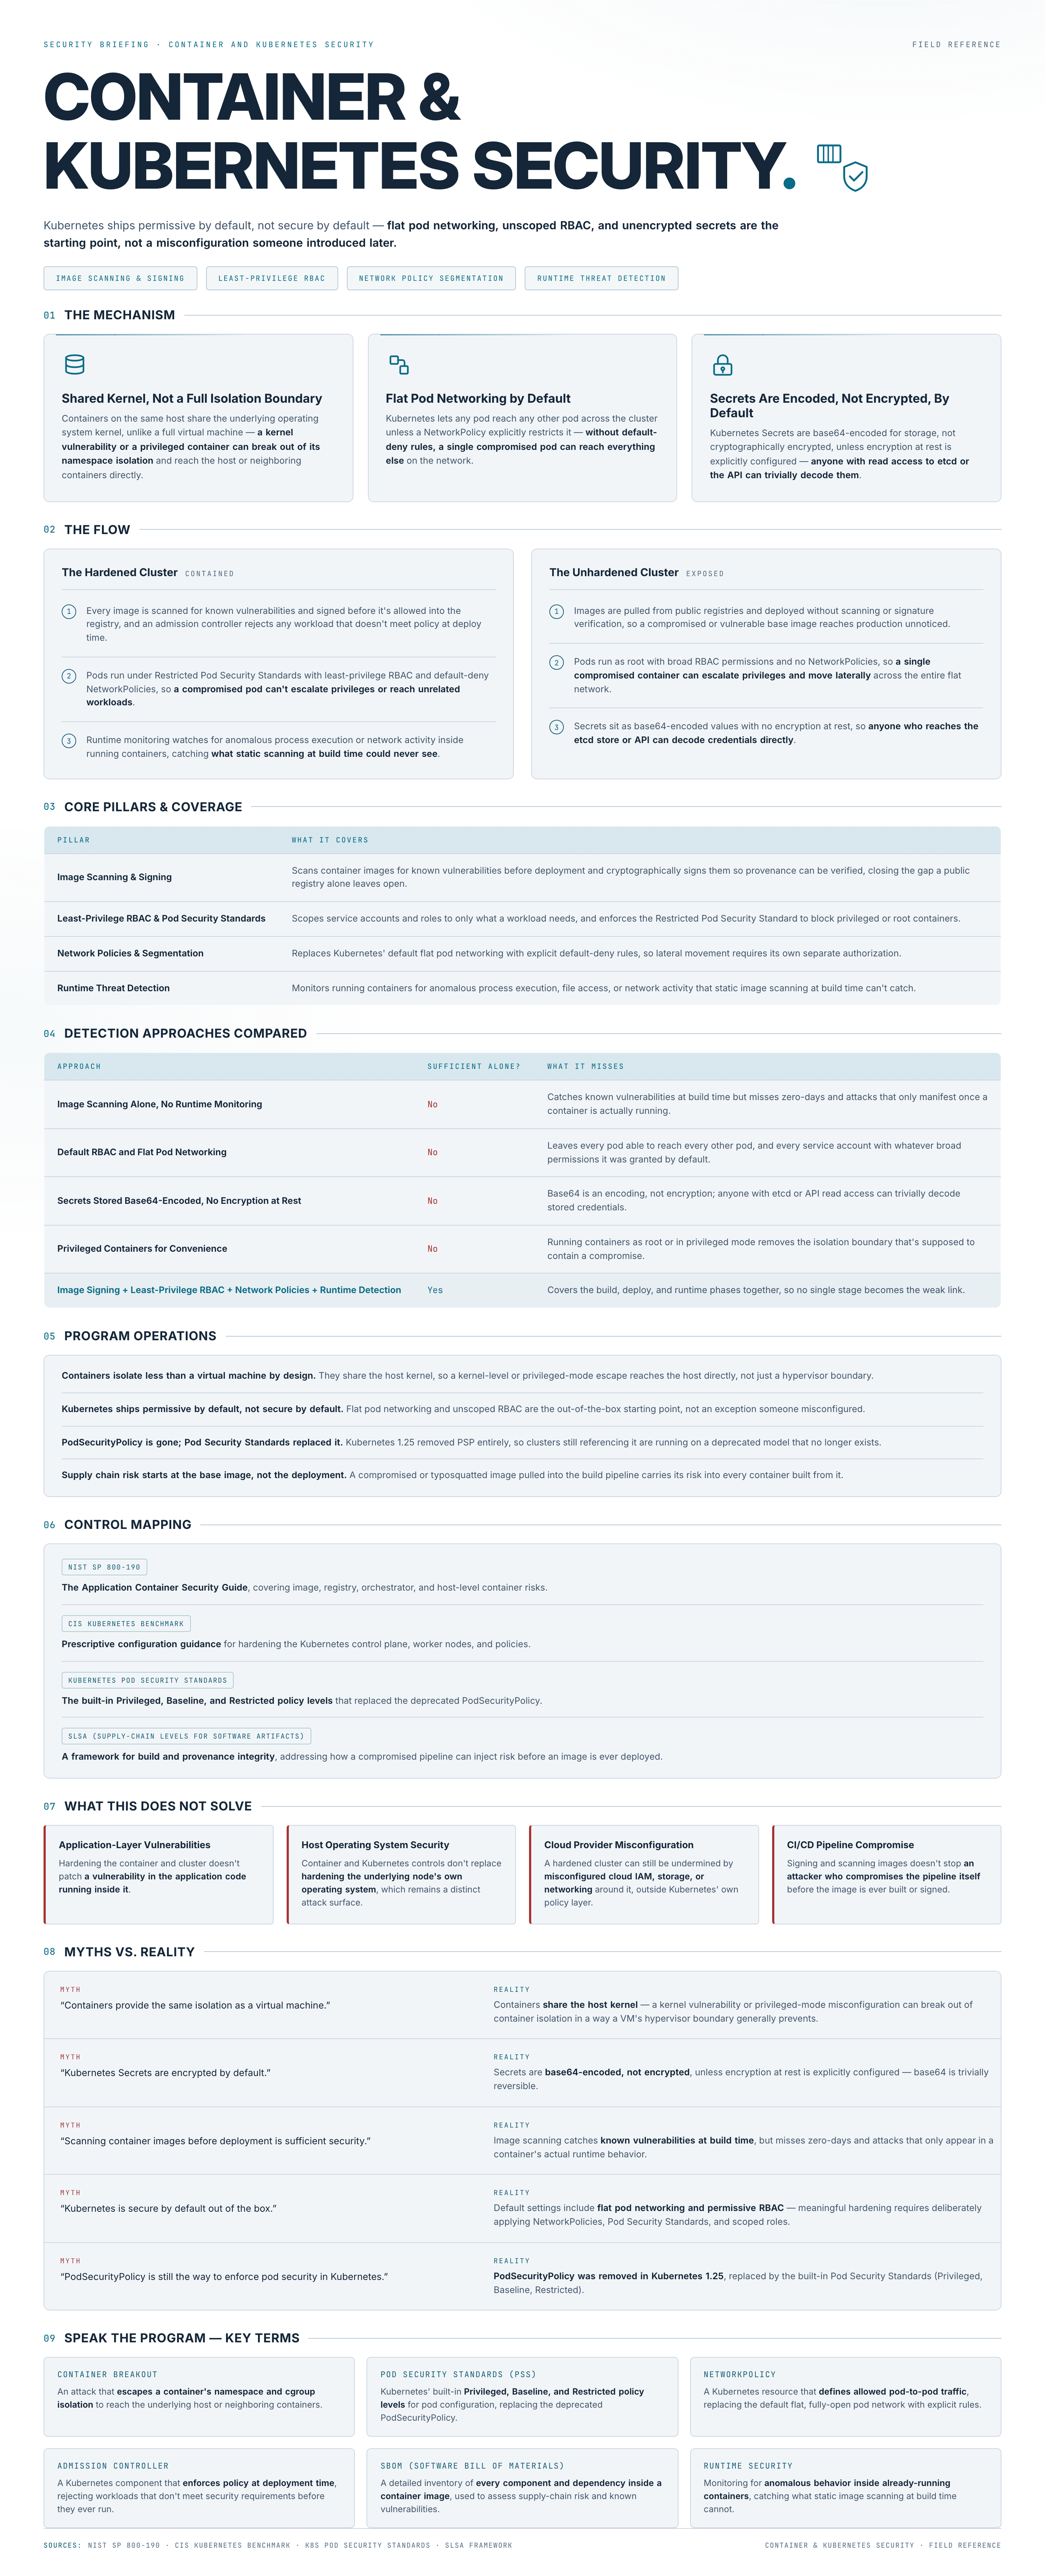
Kubernetes ships permissive by default, not secure by default — flat pod networking, unscoped RBAC, and unencrypted secrets are the starting point, not a misconfiguration someone introduced later.
Downloads
- Infographic (PNG, 2880×7100, 1.6 MB)
- Field reference (PDF, 2 sheets, 473 KB)
- Infographic, light edition (PNG, 1.7 MB)
- Field reference, light edition (PDF, 477 KB)
Free to download, no sign-up. Topic 75 of 92 in the series.